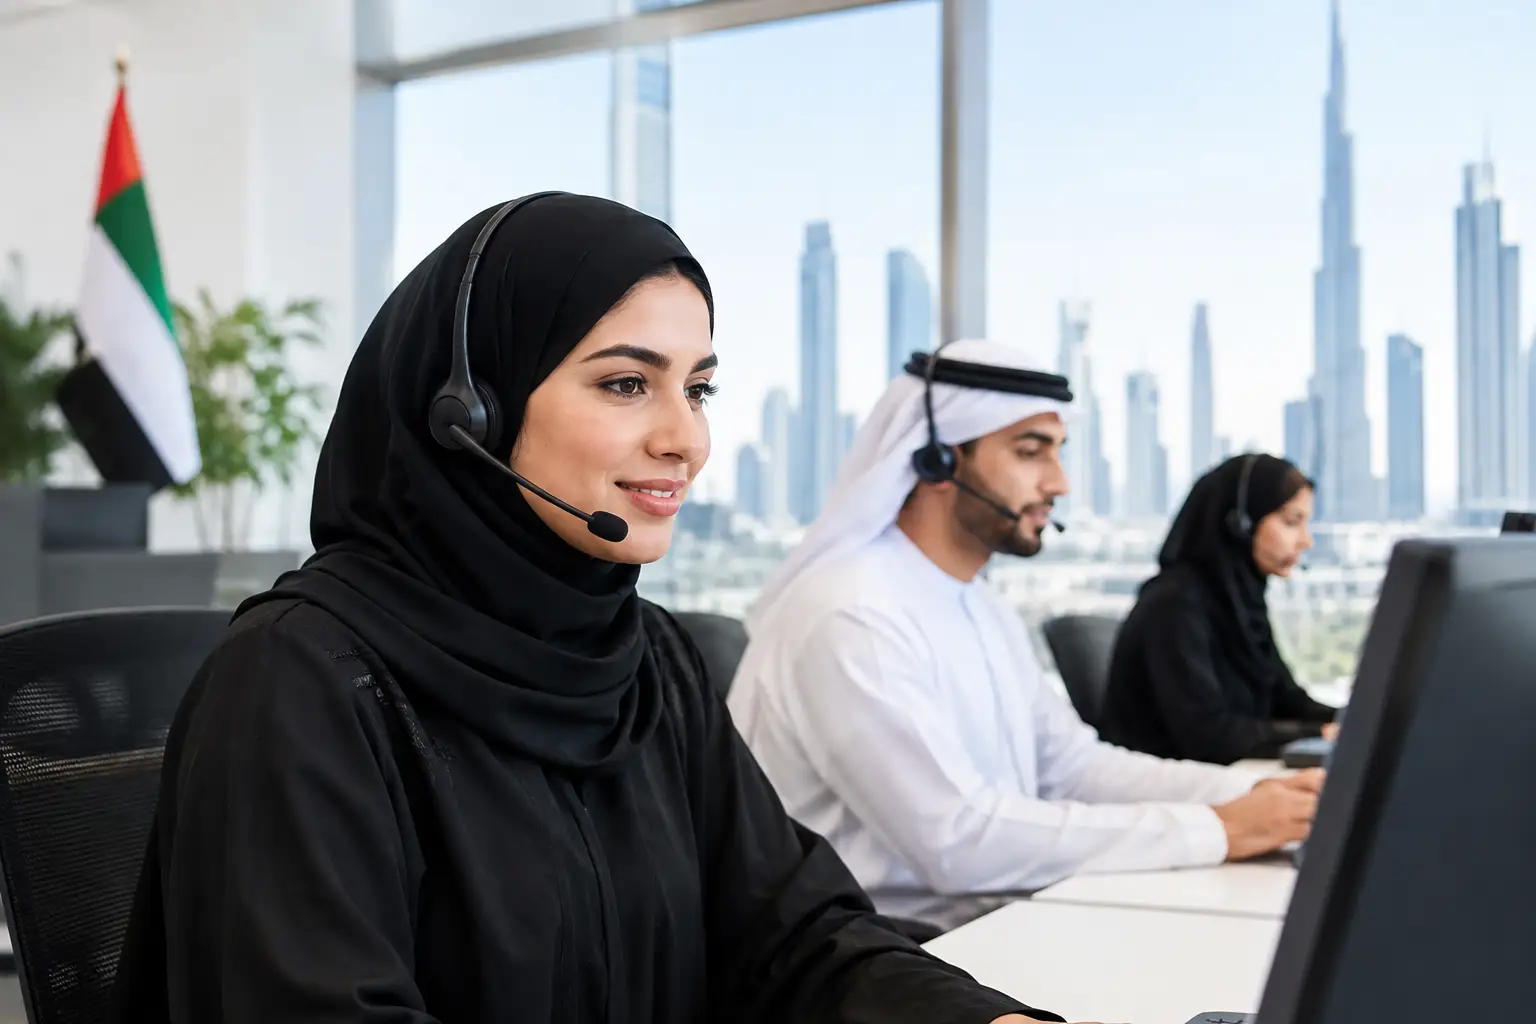
A contact center can add WhatsApp, cloud voice, CRM screen pops, and AI analytics in a matter of weeks. Telecom compliance is what determines whether those capabilities can operate reliably and lawfully once customer data, local phone numbers, call recordings, and outbound campaigns are involved. For UAE and GCC organizations, the issue is not simply choosing compliant software. It is designing the full communications environment around the right carrier connectivity, data controls, operating processes, and accountability.
For IT and customer-experience leaders, this has direct business consequences. A poorly designed deployment can create service disruption, weaken customer trust, complicate audits, and leave teams unable to prove how calls and customer information are handled. A well-designed one supports faster service, better reporting, and confident scaling across locations.
What telecom compliance actually covers
Telecom compliance is often treated as a narrow question about whether a VoIP platform is permitted. In practice, it spans the technical and operational controls around business communications. The requirements that apply depend on the organization, service model, customer location, industry, and the type of information handled.
For a UAE contact center, the foundation usually includes authorized PSTN connectivity, proper treatment of local numbering, and alignment with applicable TDRA requirements. It also includes how the business protects customer data, manages recordings, controls access, and governs outbound interactions.
A cloud application may be globally available, but that does not automatically make every calling configuration, routing method, or data flow appropriate for a UAE deployment. The crucial distinction is between a software feature and the regulated communications service that carries a customer call.
This is why compliance should be assessed across the complete call path: the agent device, contact center application, session border controller, carrier connection, recording environment, CRM integration, and retention process. One compliant component cannot correct a weak link elsewhere.
Why carrier connectivity is a compliance decision
Many projects begin with a request for lower calling costs or faster deployment. Those objectives matter, but the way voice traffic reaches the public telephone network should be settled before agents are onboarded.
Organizations that need UAE numbers and reliable inbound or outbound calling typically benefit from approved local PSTN connectivity through carriers such as Etisalat or du. Direct, correctly configured connectivity provides clearer operational ownership, dependable call routing, and a stronger basis for supporting local number use. It also avoids the uncertainty that can arise when teams rely on consumer-grade or unofficial calling workarounds.
For Microsoft Teams Direct Routing, Zoom Phone BYOC, cloud PBX, and omnichannel contact center deployments, an AnyNode SBC or comparable enterprise session border controller can play a central role. It establishes a controlled boundary between the internal communications environment and the carrier network. That boundary supports secure signaling, interoperability, dial-plan control, high availability, and better troubleshooting when a call fails.
The design choice depends on the environment. A single-site organization with modest calling volumes may prioritize rapid cloud deployment. A healthcare provider, financial institution, or multi-location operation may need greater control over call routing, resilience, recording, and integration. The right answer is not always cloud-only or on-premise-only. Hybrid architecture can be the practical option when legacy systems, local survivability, or data requirements must coexist with modern customer-experience tools.
Recording, consent, and customer-data governance
Call recording delivers real value. Supervisors can coach agents against real interactions, resolve disputes, investigate complaints, and measure service quality. Yet a recording is also customer data, and potentially sensitive customer data. The same principle applies to call transcripts, voicemail, WhatsApp conversations, screen recordings, CRM notes, and analytics exports.
A compliant design starts by defining why each category of data is collected and who needs access to it. Recording every interaction indefinitely because storage is inexpensive is not a governance strategy. Retention periods should reflect business need, contractual obligations, industry rules, and applicable legal requirements. Once the retention period ends, deletion should be controlled and auditable.
Access control matters just as much. Agents may need to review their own interactions, while quality managers need broader access and system administrators need configuration rights without unrestricted access to customer content. Role-based permissions, multi-factor authentication, access logs, and periodic permission reviews reduce unnecessary exposure.
Customer notice should be clear and appropriate to the interaction. If calls are recorded or monitored, the customer experience should not leave room for confusion. Legal teams should validate the wording, consent approach, retention policy, and cross-border data handling against the rules that apply to the organization. This is especially relevant for healthcare, insurance, banking, education, and businesses serving customers across multiple jurisdictions.
Outbound calling needs operational controls
Outbound campaigns can produce measurable pipeline and collections results, but they also introduce risk when teams prioritize volume over process. A predictive dialer, click-to-call tool, or CRM calling integration should not become a mechanism for repeated, untracked, or poorly governed contact attempts.
Contact center managers need visibility into who is calling, which number is presented, what campaign the call belongs to, and how outcomes are logged. Suppression lists, consent records where applicable, retry rules, calling-hour policies, and escalation procedures should be documented before a campaign goes live.
The controls must be practical for agents. If an agent cannot easily see a customer’s previous interactions or identify a request not to be contacted, the policy will fail in live operations. Integrating telephony with CRM and ticketing systems creates the context required to act consistently while giving managers an audit trail for coaching and dispute resolution.
Build compliance into the deployment, not the cleanup
The most effective telecom compliance programs are designed during discovery and solution architecture. Trying to add controls after numbers are activated, recordings are accumulating, and agents are taking calls is slower and more expensive.
A disciplined implementation should establish four decisions early:
- The approved carrier and PSTN connectivity model for each country and office.
- The location of voice, recording, messaging, analytics, and CRM data.
- The roles permitted to administer systems, access recordings, export reports, and change routing.
- The operational rules for recording, retention, outbound activity, incident response, and user training.
These decisions should then be reflected in the configuration, not left in a policy document. For example, a retention policy should correspond to automated deletion settings. An access policy should correspond to actual user roles. A business continuity requirement should correspond to tested failover routes and documented procedures for agents.
Training is equally important. Agents need to understand recording notices, customer authentication steps, escalation paths, and how to handle sensitive information. Supervisors need to know how to use quality tools without exporting data unnecessarily. IT teams need change-control processes for routing, integrations, SBC settings, and administrator accounts.
Compliance supports performance when it is designed well
There is a misconception that compliance slows down customer service. Poorly implemented compliance does. It creates manual work, inconsistent agent behavior, and a patchwork of disconnected systems. Well-designed controls improve operations because they standardize the information and workflows teams use every day.
A unified platform can centralize voice, email, web chat, SMS, social channels, and WhatsApp interactions while connecting them to the right customer record. QueueMetrics-style KPI analytics can reveal abandonment patterns, service levels, agent performance, and queue pressure without relying on isolated spreadsheets. Secure role-based reporting enables leaders to make decisions from governed data rather than informal exports.
The trade-off is that centralization requires careful integration design. More channels create more data flows, more identities, and more retention decisions. Organizations should avoid adopting every channel simply because the platform supports it. Start with the channels customers actually use, apply consistent governance, and expand once the operating model is proven.
Questions to ask before selecting a provider
Decision-makers should look beyond a vendor’s feature list. Ask how UAE PSTN connectivity is delivered, who owns the escalation path when calls fail, and whether the provider can support TDRA-aligned telephony practices. Confirm how recordings and customer data are hosted, accessed, retained, and deleted.
It is also worth asking whether the partner can integrate the communications environment with the CRM, ticketing, ERP, identity provider, and reporting tools already used by the business. A deployment is only as reliable as its integration points and operating support. For many organizations, 24/7 service coverage, documented incident handling, staff training, and ongoing managed services are more valuable than a low initial license price.
Cloud Move approaches telecom projects as an end-to-end implementation responsibility: solution design, carrier connectivity, contact center configuration, SBC expertise, integration, training, and continued support. That model helps organizations avoid the gaps that appear when each layer is delivered by a different party.
The practical goal is not to turn every communications decision into a legal review. It is to create an environment where compliant behavior is the easiest behavior for agents, administrators, and managers. When the technology, carrier model, and operating processes point in the same direction, customer engagement can scale without leaving governance behind.